
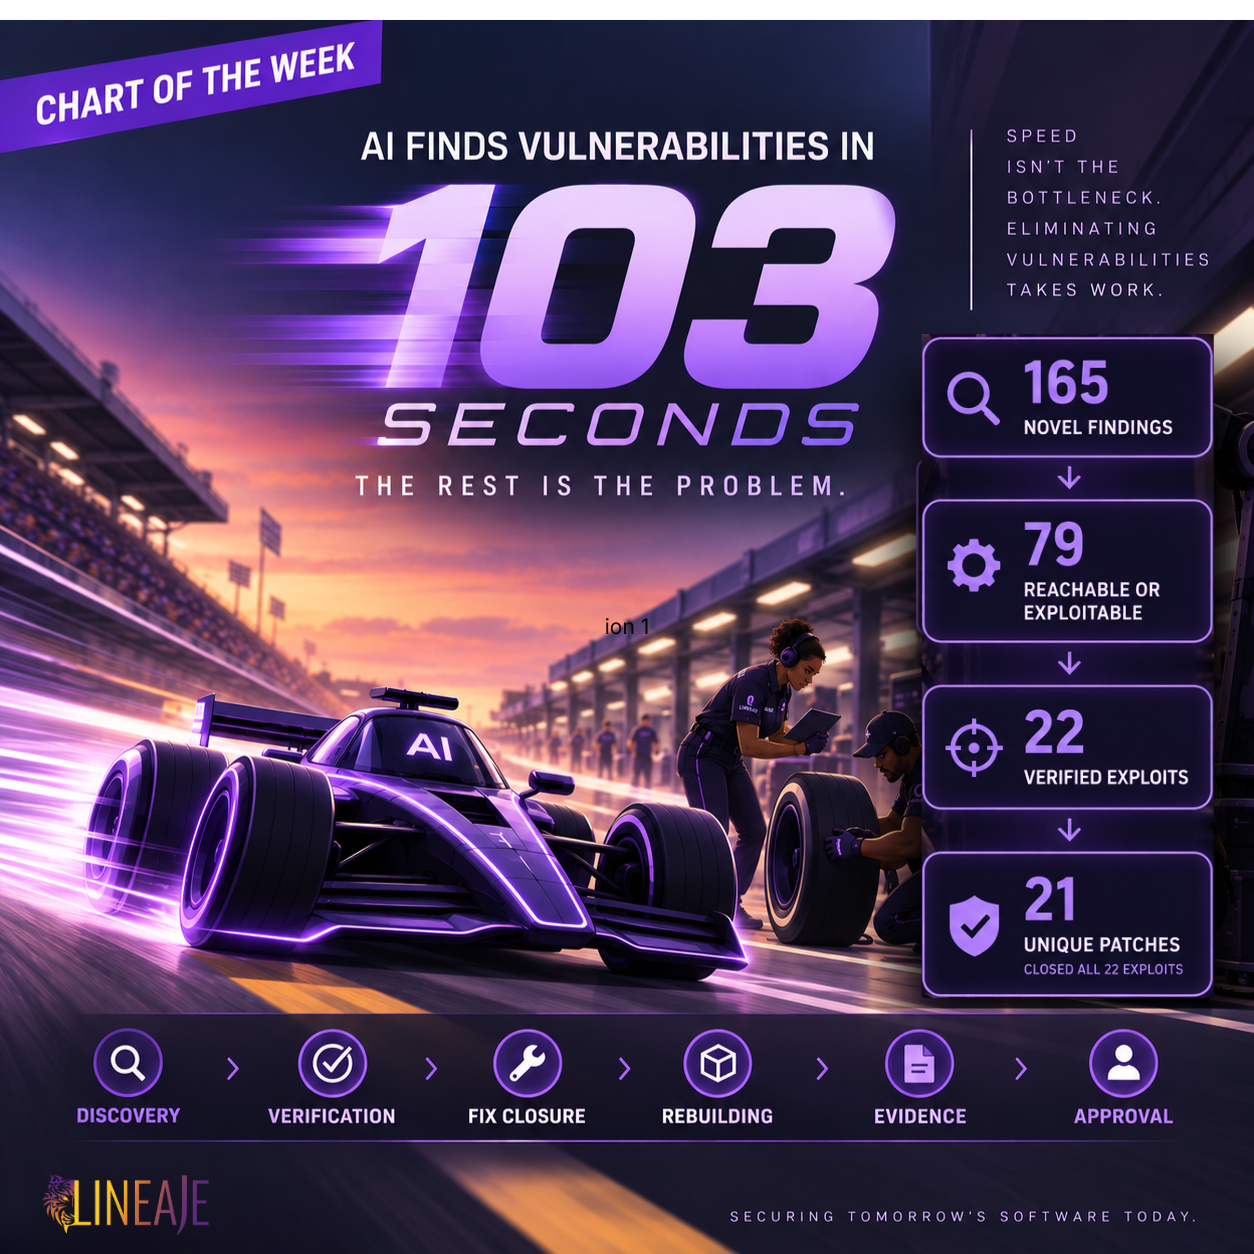
Median nonzero frontier-model runtime in Lineaje's May 2026 find/fix benchmark.
AI is making vulnerability discovery extraordinarily fast. In Lineaje's May 2026 find/fix benchmark, the median nonzero frontier-model runtime was approximately 103 seconds.
But discovery speed wasn't the real bottleneck. What came next was.
Across a broader assessment of 29 Python, Java and C++ projects, Frontier Defense produced 165 novel findings. Of those, 79 were reachable or exploitable and 22 were verified exploits. 21 unique patches closed all 22 exploits.
Finding something quickly is only the beginning. The operational work still includes verification, fix closure, rebuilding, evidence and approval. In other words, AI can accelerate the finding—but organizations still have to determine what's real, close the vulnerability, rebuild affected software, produce evidence and make risk-bearing decisions.
Security has spent years trying to improve detection speed. AI may be solving that problem faster than organizations are solving what happens after detection. Adding machine-speed discovery to a remediation process that still depends on verification, systems and human judgment doesn't necessarily reduce risk.
It can create a faster-growing backlog. The new data reinforces the problem: 52% of novel findings did not survive judging as reachable or exploitable—meaning more than half of that queue never needed to reach developers.
The next security advantage won't come from finding the most vulnerabilities. It will come from closing the loop from find → verify → fix → prove. Finding faster is not the same as becoming secure faster.
Explore the Continuous Vulnerability Elimination Factory →
Sources: Build Secure or Be Forever Insecure, Executive Summary and pp. 18–19. Lineaje May 2026 find/fix benchmark: median nonzero runtime of ~103 seconds. Frontier Defense: Vulnerable Code In, Verified Patches Out: Frontier Defense assessment across 29 Python, Java and C++ projects: 165 novel findings; 79 reachable or exploitable; 22 verified exploits; 21 unique patches closing all 22 exploits.
