

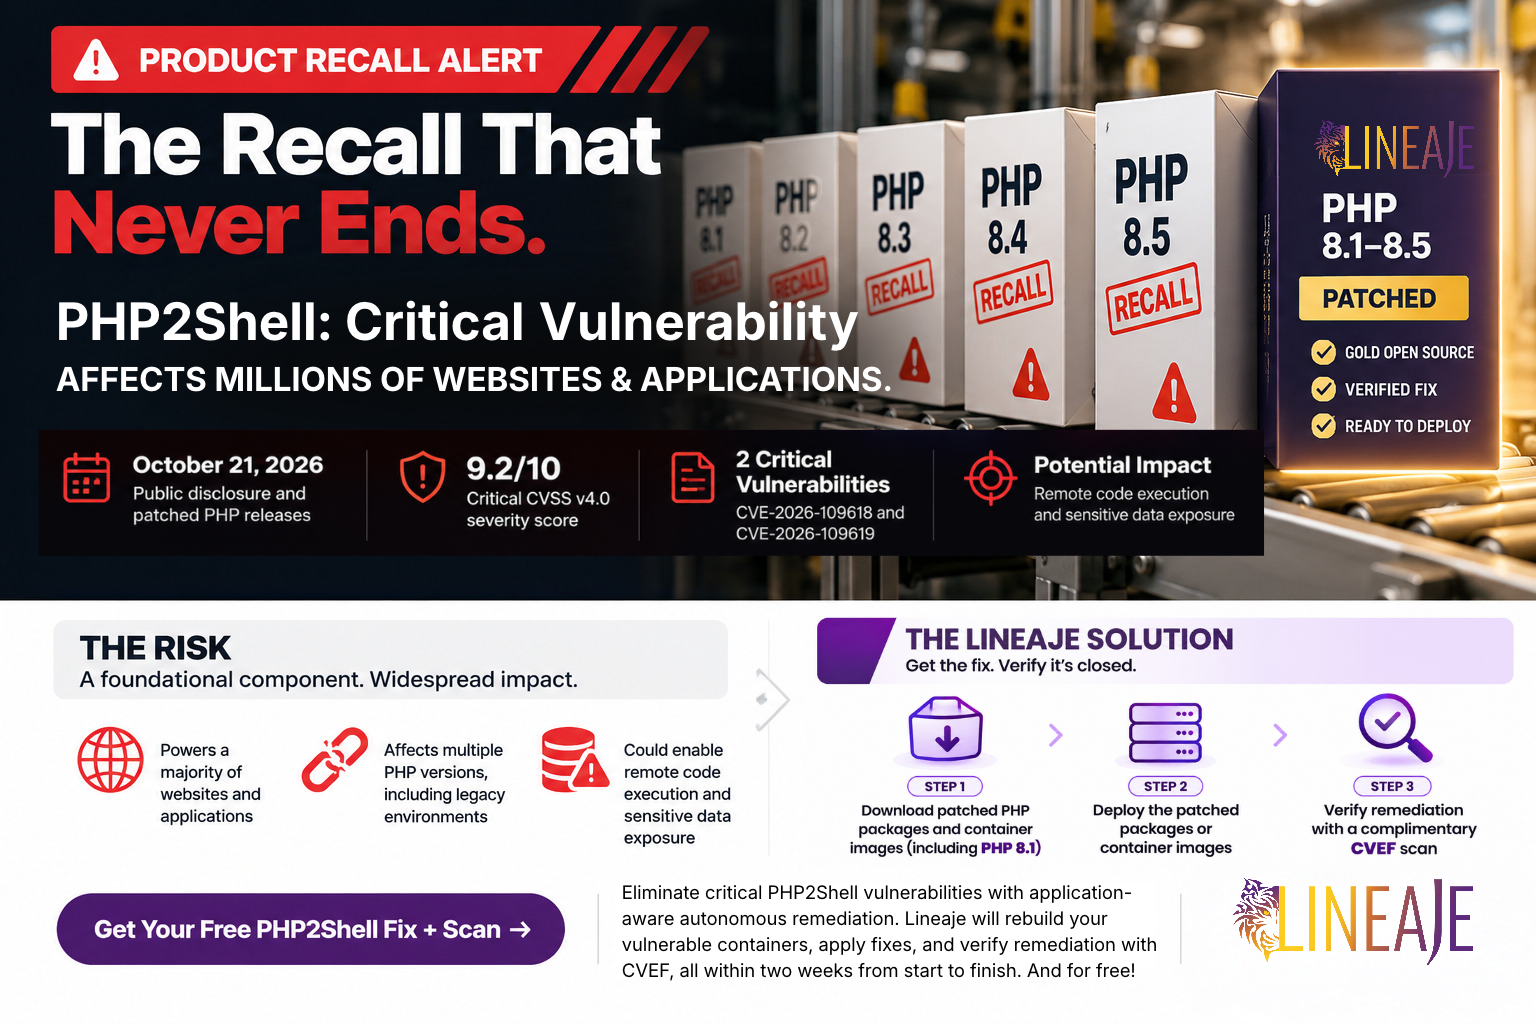
Imagine a manufacturer recalling a defective product—but no longer offering repairs for older models. That's the PHP2Shell dilemma.
Patches are available for supported PHP versions, but organizations running end-of-life versions, including PHP 8.1, face a bigger challenge: How do you eliminate exploitable vulnerabilities when upstream security fixes are no longer available?
Software doesn't disappear when vendor support ends. Legacy components remain embedded in websites, applications, servers, and container images—sometimes hidden several layers deep.
The vulnerability may be known. The fix may not be readily available for every version still in use.
Traditional vulnerability management identifies affected software. But knowing what's vulnerable doesn't eliminate the risk.
PHP2Shell? We'll fix it in 2 weeks.
Lineaje will apply application-aware fixes, rebuild vulnerable containers, and verify remediation with CVEF, all within two weeks.
https://www.lineaje.com/php2shell-vulnerability-scan
*Offer conditions may apply.
