
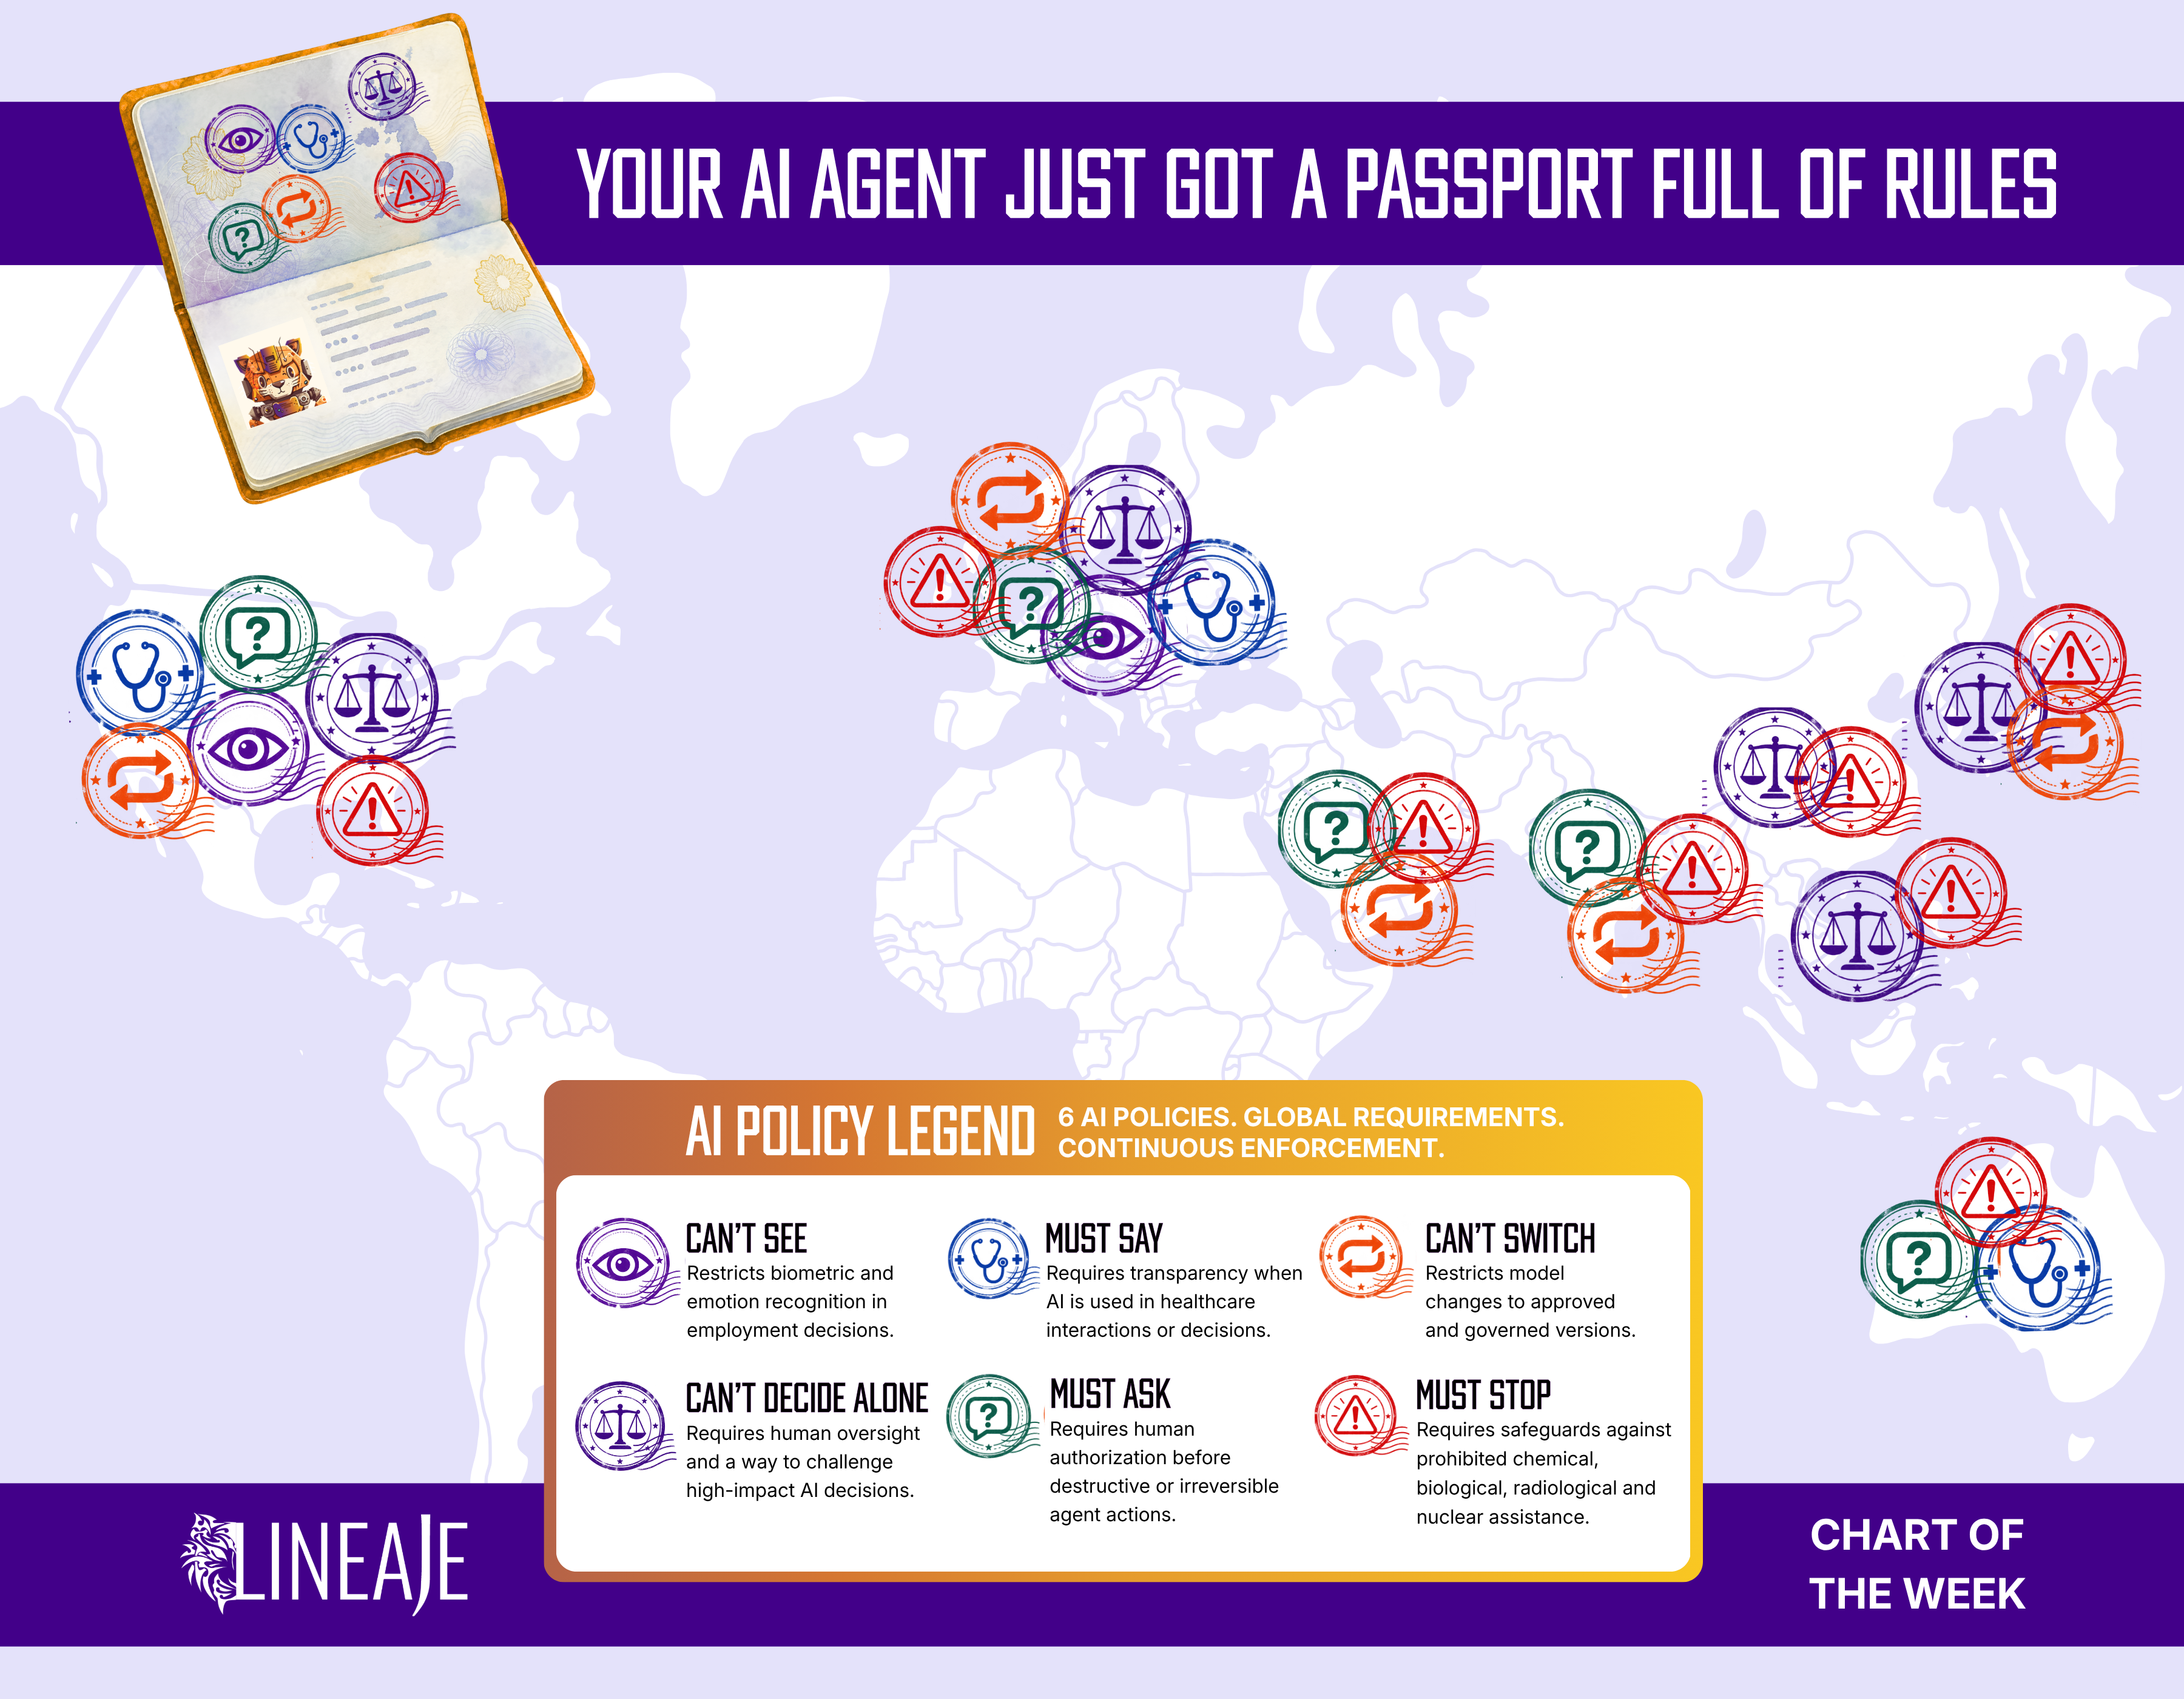
From Europe to the U.S. to Asia-Pacific, AI regulation is moving beyond broad principles and into increasingly specific requirements governing what AI systems can see, say, decide and do.
The EU AI Act alone defines four levels of AI risk and prohibits nine categories of AI practices, including certain uses of emotion recognition, biometric categorization and real-time remote biometric identification. Its prohibited-practice rules have applied since February 2025, while new AI transparency requirements took effect in August 2026. (source: Digital Strategy)
And Europe is the only part of the picture. Across jurisdictions, organizations are confronting requirements around AI transparency, human oversight, automated decisions, model governance, data access, and high-risk activity.
For an enterprise deploying AI agents, those requirements don't stay neatly inside a compliance document. They make decisions the AI system has to make.
Can I access this? Do I have to disclose this? Can I make this decision? Do I need human approval? Am I allowed to use this model? Do I have to stop?
That is the shift:
AI compliance is moving from what organizations document to what AI systems are actually allowed to do.
Consider what regulatory requirements can look like when translated into behavioral boundaries for AI:
These are not six isolated compliance problems. A single AI system may operate across jurisdictions, use cases, and regulatory frameworks at the same time.
The EU illustrates the complexity. Its AI Act distinguishes four risk levels, and obligations differ by system, use case, and risk classification. High-risk areas include employment, biometrics, critical infrastructure, education, and migration, among others. Digital Strategy
Static compliance checklists weren't designed for that kind of environment.
An AI agent doesn't stop at a regulatory border.
It can call a model hosted in one region, access data governed in another, invoke a third-party tool, communicate with another agent, and take action inside an enterprise system — potentially within seconds. And the regulatory landscape keeps shifting beneath it.
In the EU alone, different provisions of the AI Act have taken effect on different timelines: prohibited practices began applying in February 2025, general-purpose AI obligations in August 2025, transparency requirements in August 2026, and many high-risk AI requirements are scheduled to apply beginning in December 2027. (source: Digital Strategy)
The policies governing AI behavior need to move just as dynamically.
UnifAI helps organizations Discover their AI assets, Derive applicable policies from global requirements, Defend AI interactions by enforcing those policies, and Demonstrate continuous compliance with evidence of what happened and which controls were applied.
Because the next phase of AI compliance isn't simply knowing the rules. It's making sure your AI agents can follow them.
COTW Data Source → Finding Vulnerabilities Is No Longer the Hard Part | Frontier Defense: Vulnerable Code In, Verified Patches Out | By: Javed Hasan, CEO and Co-founder of Lineaje
